

Gitea shipped v28.0.0 this morning, and the version number is the first piece of news: the project dropped the historical 1. prefix, so this release is 28.0.0 rather than 1.28.0. The second thing worth knowing is where your upgrade checklist changes. Three lines are flagged breaking, and one of them touches the network behavior of migrations, mirrors and other Git operations.
The breaking lines
Git network operations now route through an internal proxy that applies Gitea’s egress settings to the connections it makes itself. The practical ask is to review your allow and block lists before upgrading, because the proxy enforces them on paths that previously went direct. Actions gains RUN_RETENTION_DAYS, so old workflow runs can delete themselves on a schedule. And the build matrix narrows: release binaries no longer include 32-bit x86 or gogit builds, the Snap is no longer built for armhf, and download filenames have lost their OS suffix (gitea-28.0.0-windows-amd64.exe), which is one line to fix in somebody’s download script.
The upgrade recipe in the announcement is the usual one: read the breaking changes, back up, replace, restart.
The security column, half-told for now
The release contains security fixes, and the project is deliberately not saying which yet. The blog post promises details in about a week, to give people time to upgrade first, which is a disclosure habit worth naming. What the changelog already shows: invalid and duplicate Git objects are rejected on push, SSH public keys are identified by fingerprint, cancelled and unapproved fork PR runs stay behind the approval gate, and repository-scoped authorization is enforced for team access, deletion and package unlinking. A denial-of-service in golang.org/x/crypto’s SSH code is patched behind it.
The features worth a look
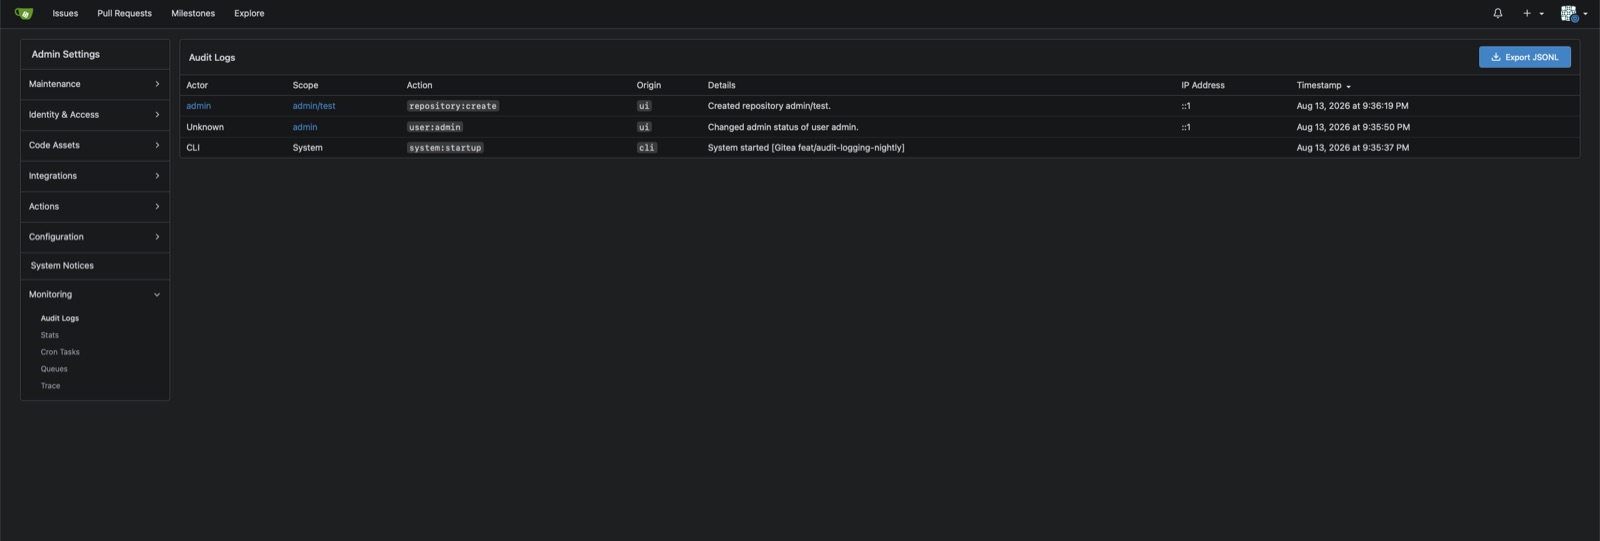
Audit logging is the headline feature. It adds an admin page under Monitoring that records actor, scope, action, origin, IP address and timestamp for security-relevant events, with JSONL export at the top. Bot accounts can now be managed from the admin UI, API and CLI. Deploy tokens arrive for HTTPS access, administrators can impersonate users (with a banner to make that obvious), personal access tokens can be regenerated, and code-owner approval rules can block merges while reviews are pending. The UI gets a quick repository switcher, WebSocket notifications replacing the old SSE stream, search and extension filters in the diff sidebar, and a build queue view for Actions.
My read
The version jump will trip a script or two, and the breaking list is short enough to actually read before upgrading. The audit log is the feature small instances have been asking for, and the egress proxy is the kind of thing a reviewer would have flagged anyway. Shipping the fixes first and the write-up a week later is the right order for a disclosure, even if it leaves the changelog looking mysterious. Back up, read the three breaking lines, and this is an easy major.
Source: the v28.0.0 release notes and the release announcement.